
Okay, so check this out—I’ve been messing with cold storage for years. Wow! My instinct said hardware wallets were the obvious answer. But something felt off about the usual USB sticks and seed-phrase notebooks that everyone swears by. On the one hand, they work; on the other hand, they invite comical mistakes and stress that you only notice when it’s too late.
Here’s what bugs me about typical setups: people treat private keys like passwords, but they behave nothing like passwords. Seriously? A lost seed phrase is a catastrophic event. Initially I thought you’d just write it down and be done. Actually, wait—let me rephrase that: I thought the system made sense at first glance, though deeper use exposes many failure modes. For example, voice-activated assistants, hidden cloud backups, curious relatives—small things that add up into risk.
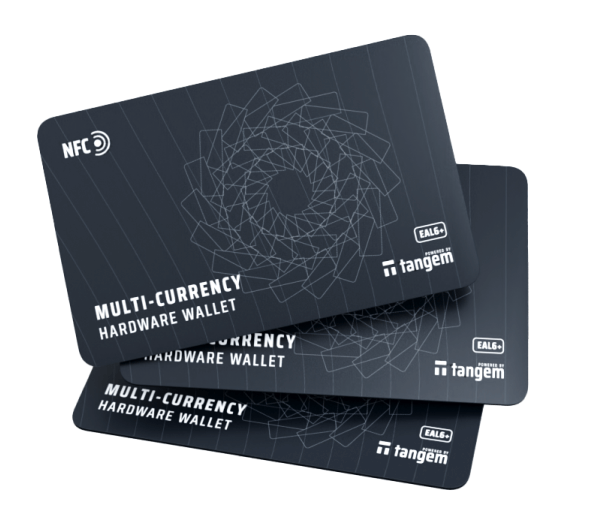
So I started carrying a different kind of device. It’s a smart-card style hardware wallet that fits in a wallet like a credit card. Whoa! The first time I tapped it, I had that kid-in-a-candy-store moment. My reaction was half excitement, half relief. The design is barely invasive—no cables, no tiny screens to squint at. That simplicity matters: you use it, or you forget about it, but it’s still protecting your keys.
What makes smart-card wallets different
Short version: they treat the private key as a piece of hardware, not text. That shift seems small, but it’s huge. Medium-length sentences here to explain: the private key never leaves the card, transactions are signed inside the secure element, and the card communicates only what it needs to—which is usually just the signed transaction. Long thought: because the signing happens on a sealed chip, where an attacker would need physical access plus side-channel expertise to compromise things, the overall attack surface is far smaller than a phone that runs dozens of apps and gets phishing links all day.
My approach is pragmatic. I’m biased, sure—I like elegant hardware. Yet I’m also cautious about lock-in and vendor risk. There’s a balance between trust in a manufacturer and trust in your own custodial practices. On one hand, you want convenience. Though actually, you also want provable isolation of your keys. For a lot of folks, smart cards walk that line well enough.
Check this out—if you care about multi-currency support, smart-card devices have come a long way. They no longer support only one chain. Instead, they often implement multiple wallets or standards, and some even let you manage dozens of coins without exporting keys. Something I like: you don’t need to memorize derivation paths or run command-line tools. It works in a mobile wallet, via NFC, with the signing done on the card itself.
I’m not 100% sure every model is equally secure. There are trade-offs. Some devices prioritize usability at the cost of certain advanced features. Others are power-user focused, a bit fiddly, and that can make everyday use unpleasant. I do know this: if you can’t use it comfortably, you’ll make mistakes. Very very important to pick hardware you actually want to carry.
Private keys: protecting the crown jewels
Think of private keys as offline bank vaults. You still need redundancy. You still need a recovery plan. But you also want to minimize exposure. Hmm… my first instinct was to copy the seed in multiple places. That felt sensible. Then I realized spreading paper backups around invokes different risks—fire, theft, bad handwriting. The smart-card model reduces the need to baby-sit multiple copies while keeping the key isolated.
There’s also the human factor. People are sloppy when they’re tired. They forward QR codes, they send screenshots. They forget why they wrote a mnemonic on a Post-it that now floats around the office. These behaviors are predictable. So a system that removes the temptation—by making keys non-exportable, by enabling tap-to-sign mechanics, and by working smoothly with your phone—has real practical benefits.
One caveat though: not all smart cards are created equal. Certification, hardware architecture, and the fallback recovery method matter. If your fallback is a single-point recovery phrase stored in a cloud note, well, that’s defeating the purpose. On the flip side, some smart cards incorporate social recovery or multi-factor designs that make recovery safer without undermining security.
Real-world scenarios that changed my mind
I once helped a friend recover from a phishing incident. It was messy and stressful, but instructive. Quick summary: they clicked a fake link, approved a malicious transaction, and lost funds. After that, they switched to a card-based approach. It wasn’t magic. It was fewer opportunities to approve dangerous transactions because the card required explicit consent and a tactile action. My takeaway: friction can be a feature, not a bug.
Also—(oh, and by the way…)—I’ve tested a handful of cards under different conditions: airport security, rainy days, and hurried coffee breaks in Brooklyn. Practical concerns like NFC reliability and card durability matter. Some cheap cards flake after months. Some premium ones are resilient. I’m picky about build quality because these things live in your wallet next to receipts and lint.
For readers who want to try one, consider a device from a vendor with a track record and clear documentation about how keys are stored and how recovery works. One practical example that fits this description is the tangem wallet, which illustrates an NFC smart-card approach that many users find intuitive and secure. I’m not shilling—just pointing out something that worked in multiple setups I’ve tested.
FAQs
How does a smart-card wallet handle multiple coins?
It depends on the firmware and supported standards. Many cards implement multiple cryptographic schemes and can generate or hold multiple accounts. The wallet app acts as the interface, enumerating supported coins and letting you sign transactions for each one without ever exposing the private key.
What happens if I lose the card?
Ideally, you set up a recovery method ahead of time—this might be a Shamir backup, a secure mnemonic stored offline, or a social recovery mechanism. Don’t wing it. If the recovery relies on a single cloud-stored seed, you’ve moved the risk rather than eliminated it.
Okay, final thoughts—I’m more optimistic now than I was five years ago. The tech evolved. The user experience improved. There are still risks. Long story short: if you want low friction plus strong protection, a smart-card hardware wallet is worth exploring. My instinct says it’s the direction for many users. But be careful, read the docs, and plan your recovery. You can’t outsource responsibility completely; you can only design it out of easy reach for attackers.